Topics in this domain
- ISACA Code of Professional Ethics
- ITAF: The Standards Framework
- Standards vs. Guidelines vs. Tools
- Auditor Independence and Objectivity
- Audit Charter: Purpose and Contents
- Audit Testing: Compliance vs. Substantive
- Financial vs. Operational vs. Integrated Audits
- Forensic and Specialized Audits
- Risk-Based Audit Approach
- Inherent, Control, Detection, and Audit Risk
- Audit Universe and Annual Audit Plan
- Audit Objectives, Scope, and the Audit Program
- Types and Reliability of Audit Evidence
- Sampling: Statistical vs. Non-Statistical
- Sampling Terms: Confidence Level, Tolerable Error and Friends
- Interviews, Observation, and Walkthroughs
- CAATs and Data Analytics
- Continuous Auditing and Monitoring
- Preventive, Detective, Corrective Controls
- General vs. Application Controls
- Compensating Controls and Segregation of Duties
- Materiality and Evaluating Findings
- Audit Report Structure and Communication
- Follow-Up and Management Action Plans
- Control Self-Assessment (CSA)
- Audit Quality and Using Other Experts' Work
Continuous Auditing and Monitoring
From yearly check-ups to a heart monitor
A traditional audit is like an annual check-up. It’s thorough, but a problem that starts in February might not be found until the next January. Continuous auditing is like wearing a heart monitor: automated checks run all the time, and the auditor hears about trouble within days.
Monitoring vs auditing
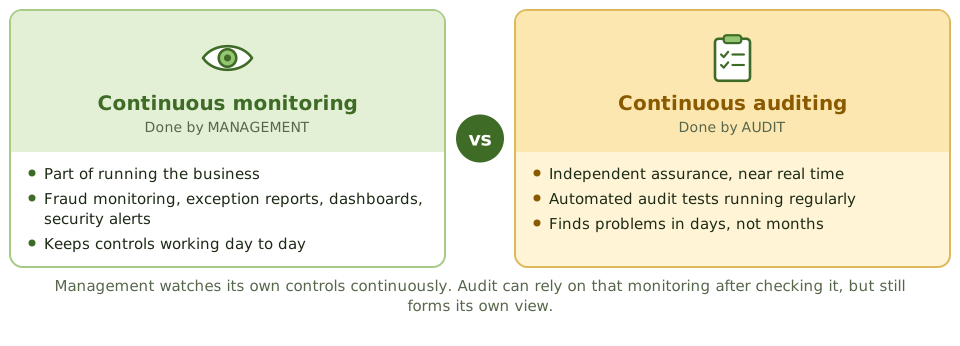
Continuous monitoring is done by management. It’s part of running the business: fraud monitoring tools, automated exception reports, risk dashboards, security alerts.
Continuous auditing is done by audit. It’s a way of gathering audit evidence regularly and automatically, so assurance is close to real time.
They connect. Where management’s monitoring is good, the auditor can evaluate it and rely on it, which reduces direct testing. But it never replaces the auditor’s own independent view.
Why bother?
- problems are found sooner, before they grow
- more transactions are tested, often all of them
- it suits paperless, high-volume businesses such as banking, payments and e-commerce
- auditors spend less time on repetitive testing and more on judgement
It needs highly automated systems, reliable general controls, audit tools that run without manual effort, and someone who acts on what’s flagged.
The online audit techniques
These are pieces of audit logic placed inside, or connected to, business systems. The exam usually describes what a technique does and asks for its name.
| Technique | What it does | Think of it as… |
|---|---|---|
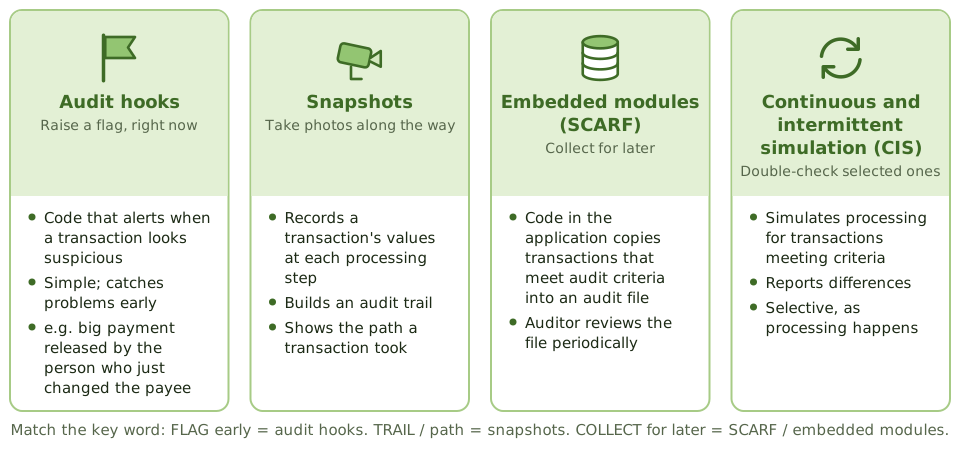
| Audit hooks | Embedded routines that flag suspicious transactions so they can be looked at before errors grow | A smoke alarm |
| Snapshots | Record images of a transaction at points along its processing path | Photos at each stage of a journey |
| Embedded audit modules / SCARF (systems control audit review file) | Code inside the application that copies transactions meeting audit criteria into a separate audit file | A filter that collects the interesting ones |
| Integrated test facility (ITF) | A dummy entity in production; the auditor’s test transactions are processed alongside real ones | A mystery shopper |
| Continuous and intermittent simulation (CIS) | During processing, simulates the handling of transactions that meet set criteria and reports differences | A spot-check double-calculation |
A simple way to tell them apart:
- Flag suspicious things early, with little complexity → audit hooks.
- Show the path or create an audit trail → snapshots.
- Collect transactions for later audit review → SCARF / embedded audit modules.
Example. A bank sets up an audit hook that alerts internal audit whenever a payment over a threshold is released by someone who also changed the beneficiary’s bank details in the previous 24 hours. Auditors review each alert within a day, instead of discovering the pattern at the year-end audit.
How the exam asks about it
| If the question asks… | The answer is usually… |
|---|---|
| Main benefit of continuous auditing | Earlier detection; more transactions tested |
| Prerequisite for continuous auditing | Highly automated systems with reliable controls |
| Technique that flags suspicious transactions early | Audit hooks |
| Technique that provides a transaction audit trail | Snapshots |
| Who is responsible for continuous monitoring? | Management |
| Can audit rely on management’s continuous monitoring? | Yes, after evaluating it; it reduces but doesn’t replace audit testing |
In short
- Continuous monitoring is done by management as part of running controls. Continuous auditing is done by audit to give ongoing, independent assurance.
- Continuous auditing shortens the gap between something happening and the auditor knowing about it.
- It needs highly automated systems, reliable general controls, and audit tools built into or connected to the systems.
- Audit hooks flag suspicious transactions for immediate attention. They're simple and catch problems early.
- Snapshots record a transaction's values at each step, giving an audit trail.
- Embedded audit modules (SCARF) collect transactions that meet audit criteria into a file for later review.
- Continuous and intermittent simulation (CIS) re-checks selected transactions as they're processed.
Exam traps
- Management's monitoring can reduce audit's testing, but never replaces the auditor's independent view.
- 'Flag suspicious transactions early, with little complexity' → audit hooks.
- Snapshot = audit trail of the path. SCARF = collecting transactions for later.
- Continuous auditing needs automated systems; it doesn't suit manual, paper-based processes.
Slides
Click the slide and use the arrow keys. F toggles full screen.
Monitoring vs auditing
The online audit techniques
These are pieces of audit logic placed inside, or connected to, the business systems. The exam usually describes what a technique does and asks for its name.