Topics in this domain
- ISACA Code of Professional Ethics
- ITAF: The Standards Framework
- Standards vs. Guidelines vs. Tools
- Auditor Independence and Objectivity
- Audit Charter: Purpose and Contents
- Audit Testing: Compliance vs. Substantive
- Financial vs. Operational vs. Integrated Audits
- Forensic and Specialized Audits
- Risk-Based Audit Approach
- Inherent, Control, Detection, and Audit Risk
- Audit Universe and Annual Audit Plan
- Audit Objectives, Scope, and the Audit Program
- Types and Reliability of Audit Evidence
- Sampling: Statistical vs. Non-Statistical
- Sampling Terms: Confidence Level, Tolerable Error and Friends
- Interviews, Observation, and Walkthroughs
- CAATs and Data Analytics
- Continuous Auditing and Monitoring
- Preventive, Detective, Corrective Controls
- General vs. Application Controls
- Compensating Controls and Segregation of Duties
- Materiality and Evaluating Findings
- Audit Report Structure and Communication
- Follow-Up and Management Action Plans
- Control Self-Assessment (CSA)
- Audit Quality and Using Other Experts' Work
Control Self-Assessment (CSA)
Asking the people who know best
The people who run a process every day usually know exactly where it’s weak: the workaround everyone uses, the check that gets skipped at month end. Control self-assessment (CSA) taps into that knowledge.
In a CSA, the process owners and staff assess their own risks and controls, usually in a workshop guided by an auditor.
Think of a sports team watching its own match video with the coach. The players spot their own mistakes, because they know what they were trying to do. The coach guides the discussion but doesn’t play.
The main objective is to shift some responsibility for monitoring controls to the business, so managers own their controls and audit’s coverage stretches further.
CSA vs a traditional audit
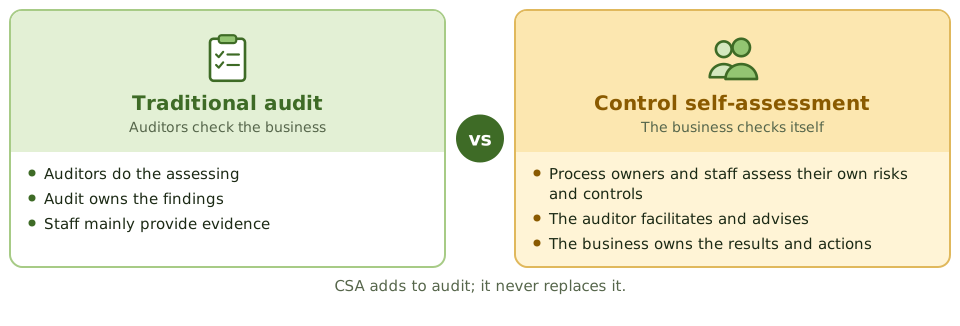
| Traditional audit | Control self-assessment | |
|---|---|---|
| Who assesses | Auditors | Process owners and staff |
| Auditor’s role | Does the work, reaches conclusions | Facilitates and advises |
| Who owns the results | Audit | The business |
| Staff involvement | Mostly providing evidence | Active participants |
How CSA is done
| Approach | How it works | Suits |
|---|---|---|
| Facilitated workshops | Groups of staff discuss risks and controls, often voting anonymously | Rich discussion; surfacing issues staff know about |
| Questionnaires or surveys | Structured questions for control owners | Many locations doing the same thing |
| Management’s own analysis | Management documents and evaluates its controls; audit reviews it | Mature control environments |
Benefits
- risks and gaps are spotted earlier, by the people closest to the process
- managers take ownership of controls and improvements
- staff understand objectives, risks and controls better
- communication between the business and audit improves
- audit covers more ground without needing many more auditors
Risks
- it’s mistaken for a replacement for audit
- participants may lack objectivity or the skills to judge controls
- ideas get raised but never acted on, which hurts morale
- it adds to the business’s workload
- sensitive issues may not come up in a group
Example. Instead of auditing all 40 branches every year, audit runs yearly CSA workshops with branch managers on cash handling, customer data and access controls. Five branches give weak answers, and those go into the audit plan for on-site testing.
How the exam asks about it
| If the question asks… | The answer is usually… |
|---|---|
| Primary objective of CSA | Shift responsibility for control monitoring to the business; leverage audit |
| The auditor’s role in CSA | Facilitator and adviser |
| Can CSA replace internal audit? | No; it supplements audit |
| Main benefit of CSA | Early detection of risks and business ownership of controls |
| Main risk of CSA | It’s treated as a replacement for audit, or improvements aren’t made |
In short
- In control self-assessment (CSA), the people who run a process assess its risks and controls themselves, usually in facilitated workshops.
- The main objective is to shift some responsibility for monitoring controls to the business, extending audit's reach.
- The auditor acts as facilitator and adviser; the business owns the conclusions.
- Benefits: risks spotted earlier, ownership of controls by the business, better awareness, wider coverage.
- Risks: being mistaken for a replacement for audit, staff lacking objectivity or skills, and improvements not being made.
- CSA results can guide audit planning, but the auditor still tests key controls independently.
Exam traps
- CSA does NOT replace internal audit.
- The primary objective is to leverage audit by shifting control monitoring to the business, not to cut audit costs.
- In CSA the auditor facilitates; the business owns the assessment.
Slides
Click the slide and use the arrow keys. F toggles full screen.
CSA vs a traditional audit