Topics in this domain
- IT Governance vs. IT Management
- Board and Senior Management Roles
- IT Steering Committee
- IT Strategy and Business Alignment
- Balanced Scorecard
- COBIT
- ITIL
- ISO 27001/27002
- COSO: ERM and Internal Control
- Policies, Standards, Procedures, Guidelines
- IT Organizational Structure and Key Roles
- Segregation of Duties in IT
- Enterprise Architecture (Zachman, TOGAF)
- Risk Management Process
- Qualitative vs. Quantitative Risk Assessment
- Risk Responses: Mitigate, Transfer, Avoid, Accept
- Risk Appetite and Residual Risk
- Maturity Models (CMMI)
- KPIs and KGIs
- Outsourcing: Benefits and Risks
- Vendor Selection, Contracts, SLAs, Right to Audit
- Cloud and Offshore Governance
- Portfolio and Resource Management
- HR: Hiring, Training, Termination
- Legal and Regulatory Compliance
- Quality Management
Board and Senior Management Roles
Who’s in charge of what?
Good governance needs clear answers to “whose job is this?”. Without them, everyone assumes someone else is handling it, and nobody does. The exam tests these roles constantly, usually by describing a decision and asking who should make it.
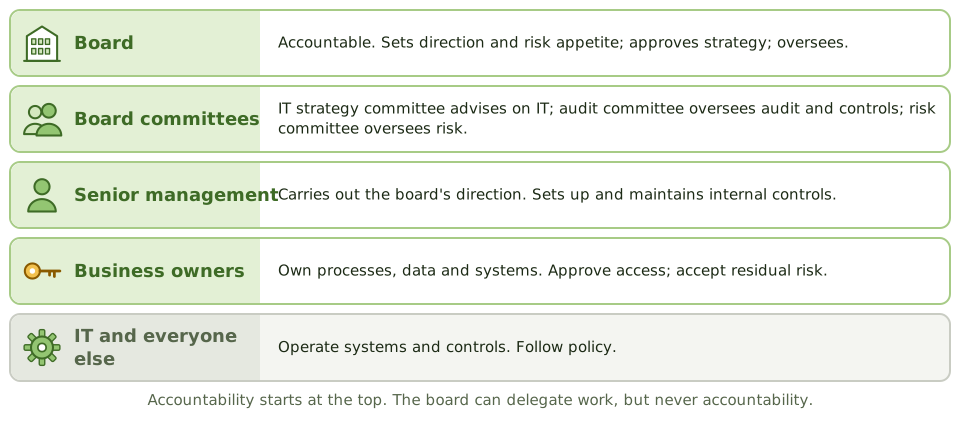
The board
The board is accountable for the organisation’s governance, including IT and information security. It can hand activities to committees and managers, but it can’t hand away accountability.
The board’s IT-related responsibilities:
- approve the business strategy and the IT strategy that supports it
- set the risk appetite, including for IT and information risk
- approve major IT investments
- monitor performance, major projects and significant risks
- make sure management has an effective control environment
Board committees
| Committee | Focus |
|---|---|
| IT strategy committee | Advises the board on IT strategy, alignment, investment and IT risk |
| Audit committee | Oversees internal and external audit, financial reporting and internal control; receives audit reports |
| Risk committee | Oversees enterprise risk, including technology and cyber risk |
Senior management
Executive management, led by the CEO, turns the board’s direction into action. It’s responsible for:
- setting up and maintaining internal controls (internal audit only checks them)
- setting up structures such as the IT steering committee
- assigning roles, including data and system owners
- providing people and money for governance and security programs
- reporting performance and risk to the board
Tone at the top
When the exam asks for the most important factor in making a governance, risk or security program succeed, the answer is very often senior management commitment and support. Without it, policies have no authority and programs have no budget.
Example. A new security policy says everyone must use MFA. The CEO refuses because it’s “annoying”. Within months, other executives opt out too, then their teams. The policy still exists on paper; the tone at the top killed it.
Other key roles
| Role | Responsibility |
|---|---|
| CIO | Leads IT, aligns it with the business, manages IT resources |
| CISO | Leads the information security program |
| Business process owner | Owns a process and its controls |
| Data owner | Classifies data, approves access, accepts risk for their data |
| Data custodian | Stores and protects data as the owner directs (often IT) |
| Users | Follow policy; use systems as authorised |
Example. An auditor finds that IT decides who can access the HR system, without asking HR. The finding isn’t that IT is careless. It’s that the data owner role is missing: HR should own the data and approve access, with IT as the custodian.
How the exam asks about it
| If the question asks… | The answer is usually… |
|---|---|
| Who is responsible for establishing internal controls? | Management |
| Who sets risk appetite? | The board |
| Most important factor in a governance or security program’s success | Senior management commitment and support |
| Who approves access to data? | The data owner |
| Role of the audit committee | Oversight of audit and internal control |
In short
- The board is accountable for governance, including IT and information security, and sets the risk appetite.
- Senior management carries out the board's direction and is responsible for setting up and maintaining internal controls.
- The IT strategy committee advises the board on IT strategy; the IT steering committee oversees delivery at management level.
- The audit committee oversees internal audit, external audit, financial reporting and the control environment.
- Business data owners decide on data classification and access; IT acts as custodian.
- 'Tone at the top' (visible senior management support) is the most important factor for governance and security programs.
Exam traps
- Responsibility for internal controls lies with management, not internal audit.
- The board can delegate activities but not accountability.
- The CISO doesn't own business data; data owners do.
- 'Most important factor for success' questions usually point to senior management support.
Slides
Click the slide and use the arrow keys. F toggles full screen.
Who's in charge of what?
Good governance needs clear answers to 'whose job is this?'. Otherwise everyone assumes someone else is handling it.
The exam tests these roles constantly, usually by describing a decision and asking who should make it.