Topics in this domain
- IT Governance vs. IT Management
- Board and Senior Management Roles
- IT Steering Committee
- IT Strategy and Business Alignment
- Balanced Scorecard
- COBIT
- ITIL
- ISO 27001/27002
- COSO: ERM and Internal Control
- Policies, Standards, Procedures, Guidelines
- IT Organizational Structure and Key Roles
- Segregation of Duties in IT
- Enterprise Architecture (Zachman, TOGAF)
- Risk Management Process
- Qualitative vs. Quantitative Risk Assessment
- Risk Responses: Mitigate, Transfer, Avoid, Accept
- Risk Appetite and Residual Risk
- Maturity Models (CMMI)
- KPIs and KGIs
- Outsourcing: Benefits and Risks
- Vendor Selection, Contracts, SLAs, Right to Audit
- Cloud and Offshore Governance
- Portfolio and Resource Management
- HR: Hiring, Training, Termination
- Legal and Regulatory Compliance
- Quality Management
ISO 27001/27002
A system for managing security
Buying a firewall doesn’t make an organisation secure. Security has to be managed: risks assessed, controls chosen, people trained, results checked and improvements made, again and again.
ISO/IEC 27001 describes how to run that management system, called an ISMS (information security management system).
Think of a gym membership. Buying equipment (controls) isn’t enough. You need a plan, regular workouts, someone checking progress, and adjustments when it isn’t working. An ISMS is the routine that keeps security fit.
27001 vs 27002
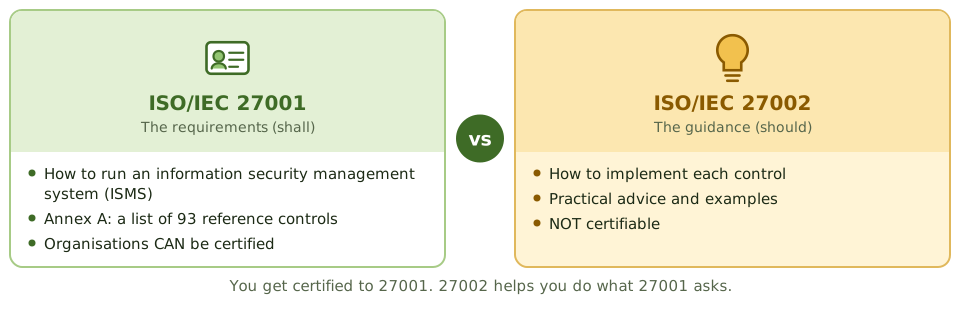
- ISO/IEC 27001 sets out the requirements for an ISMS. It’s the standard organisations get certified against.
- ISO/IEC 27002 is guidance on how to implement the security controls. It supports 27001 but isn’t certifiable.
How an ISMS works
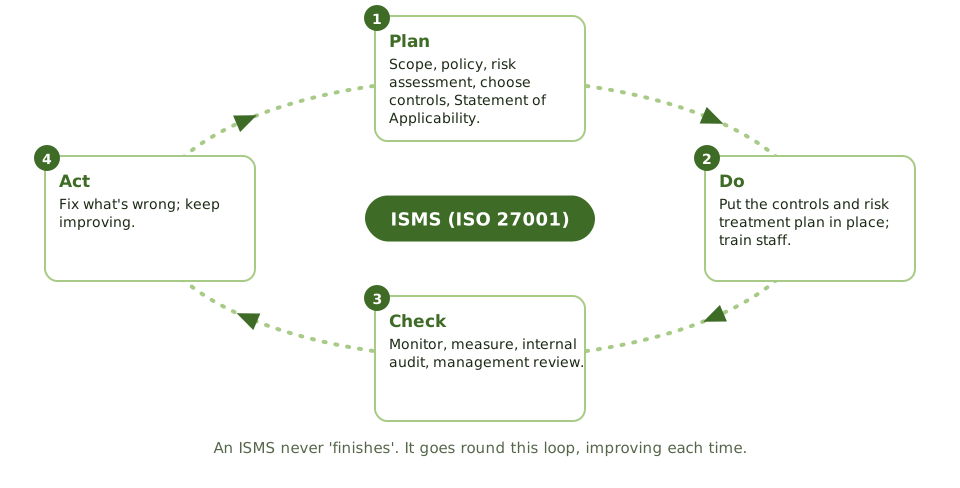
| Phase | What happens |
|---|---|
| Plan | Understand the context; define scope; management sets the policy and goals; assess risks; choose treatments and controls; write the Statement of Applicability |
| Do | Put the controls and treatment plan in place; train staff; run the ISMS |
| Check | Monitor and measure; do internal audits; management reviews |
| Act | Fix problems; keep improving |
Top management commitment is a requirement: management must set the policy, assign roles, provide resources and review the ISMS.
Annex A and the Statement of Applicability
Annex A of 27001 lists reference controls. The 2022 version has 93, grouped in four themes:
| Theme | Examples |
|---|---|
| Organisational | Policies, roles, asset management, supplier security, incident management, continuity |
| People | Screening, awareness training, disciplinary process, remote working |
| Physical | Secure areas, equipment protection, clear desk |
| Technological | Access control, cryptography, logging, malware protection, secure development, backup |
Organisations choose controls based on their risk assessment. They don’t have to implement everything.
The Statement of Applicability (SoA) records, for every Annex A control: whether it applies, whether it’s in place, and why it’s included or excluded. An auditor checks that exclusions are justified by the risk assessment.
What a certificate proves
Certification by an accredited body means the ISMS met 27001’s requirements for the certified scope, at the time of the last certification or surveillance audit. Before relying on it, check:
- the scope: does it cover the systems, sites and services you care about?
- that the certificate is current and from an accredited body
- what the latest audits found
Certification doesn’t prove every control works, and says nothing about anything outside the scope.
Example. A cloud provider advertises ISO 27001 certification. Its certificate only covers its European data centres. The customer’s data is processed in another region, so the certificate doesn’t give the assurance the customer needs, and more evidence is required.
How the exam asks about it
| If the question asks… | The answer is usually… |
|---|---|
| Which standard organisations are certified against | ISO/IEC 27001 |
| Purpose of ISO/IEC 27002 | Guidance on implementing security controls |
| Document listing applicable controls and justifications | Statement of Applicability |
| What drives control selection in an ISMS | Risk assessment |
| First thing to check when relying on a certificate | Its scope |
In short
- ISO/IEC 27001 sets out the requirements for an information security management system (ISMS). Organisations can be certified against it.
- ISO/IEC 27002 is guidance on how to implement security controls. It isn't certifiable.
- Annex A of 27001 lists reference controls (93 in the 2022 version, in four themes: organisational, people, physical, technological).
- The Statement of Applicability (SoA) records which Annex A controls apply, whether they're in place, and why any are excluded.
- An ISMS follows Plan-Do-Check-Act: risk assessment drives the choice of controls; internal audits and management reviews drive improvement.
- A certificate shows the ISMS meets 27001 for its certified scope. Always check the scope covers what you care about.
Exam traps
- You get certified to 27001, not 27002.
- Certification doesn't mean every control works; it means the management system meets the standard for its scope.
- Controls are chosen by risk assessment, not by implementing all of Annex A.
- Every exclusion in the SoA needs a justification.
- A certified data centre doesn't cover the company's software development, unless that's in scope.
Slides
Click the slide and use the arrow keys. F toggles full screen.
27001 vs 27002
How an ISMS works