Topics in this domain
- Security Governance and Roles
- Data Classification and Ownership
- Security Policies
- Privacy Principles and GDPR
- Identity Management
- Authentication Factors
- Biometrics
- Access Models: DAC, MAC, RBAC
- Logical and Privileged Access
- Cryptography Basics
- Symmetric Encryption
- Asymmetric Encryption
- Hashing and Integrity
- Digital Signatures
- PKI and Certificates
- Firewalls
- IDS/IPS
- VPN, SSL/TLS, IPsec
- Wireless Security
- Endpoint and Mobile (BYOD)
- Cloud and Virtualization Security
- Physical Access Controls
- Environmental Controls: Fire, Power, HVAC
- Social Engineering
- Malware
- Network Attacks: DoS, Spoofing, Sniffing
- Application Attacks: SQLi, XSS
- Vulnerability Management and Pen Testing
- Incident Response
- Digital Forensics and Chain of Custody
- Security Awareness Training
- Logging, SIEM, and Auditing Security
Cryptography Basics
Locks, keys and fingerprints
A combination padlock is public: anyone can buy one and see how it works. What keeps your locker safe is the combination. Cryptography works the same way: the algorithm (the lock design) is public; the key (the combination) must stay secret. And it’s only as good as how carefully you guard the combination.
The few terms you need:
- Plaintext / ciphertext: readable data / scrambled data.
- Algorithm (cipher): the mathematical method.
- Key: the secret value that controls the scrambling.
- Key length: longer keys resist brute-force guessing better.
- Block cipher / stream cipher: encrypts fixed-size blocks / a continuous stream of bits.
- Cryptanalysis: the study of breaking ciphers.
- Work factor: the time and effort needed to break the encryption.
What it can do
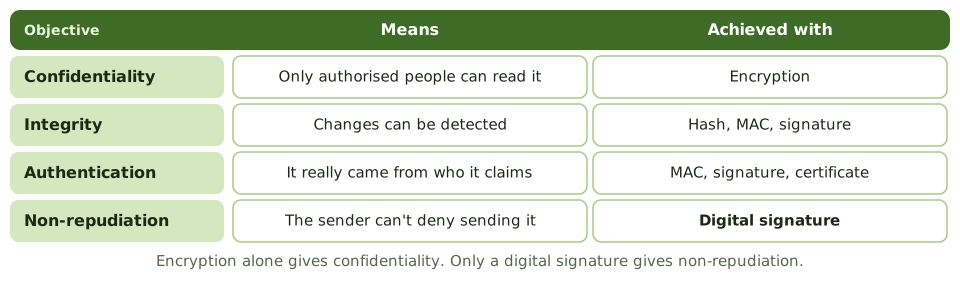
| Objective | Meaning | Technique |
|---|---|---|
| Confidentiality | Only authorised parties can read the data | Encryption (symmetric or asymmetric) |
| Integrity | Changes to data can be detected | Hashes, message authentication codes, digital signatures |
| Authentication | The source is who it claims to be | MACs, digital signatures, certificates |
| Non-repudiation | The sender can’t deny sending | Digital signatures |
Encryption on its own gives confidentiality, nothing more.
Three tools
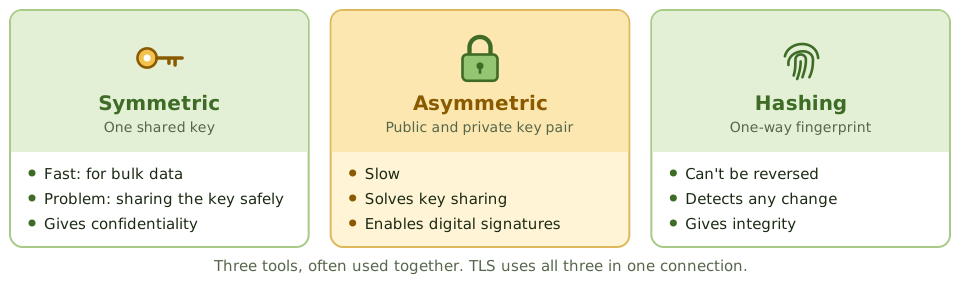
- Symmetric encryption (one shared key) is fast, so it’s used for bulk data.
- Asymmetric encryption (a public and private key pair) solves the problem of sharing keys and makes digital signatures possible, but it’s slow.
- Hashing makes a one-way fingerprint for checking integrity. It isn’t encryption and can’t be reversed.
Protocols such as TLS use all three: asymmetric crypto checks the server’s identity and agrees a symmetric session key, symmetric encryption protects the data, and hashes or MACs protect integrity.
Key management is where it fails
Most real-world crypto failures come from key management, not broken algorithms.
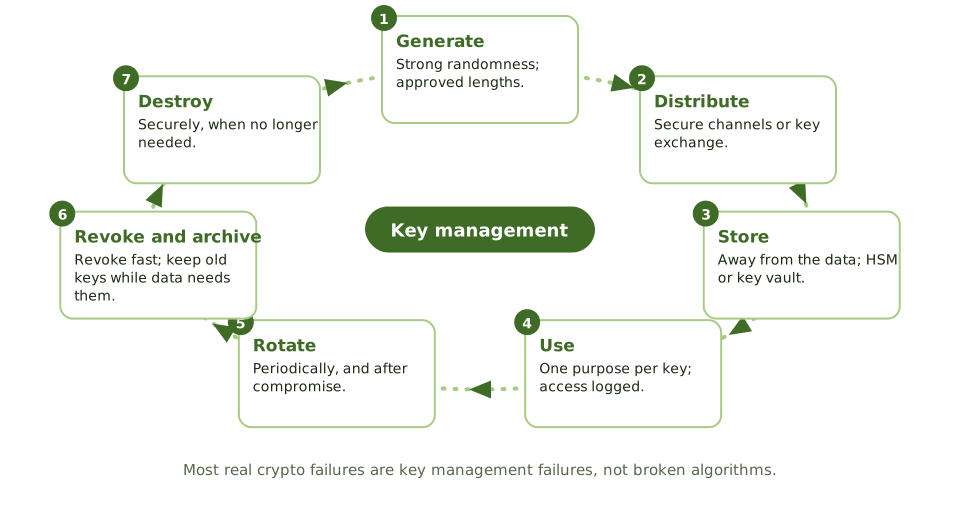
| Stage | Controls |
|---|---|
| Generation | Strong random number generators; approved key lengths |
| Distribution | Secure channels; asymmetric key exchange |
| Storage | Separate from the encrypted data; HSMs or cloud key management services; tight access |
| Use | One purpose per key; access logged |
| Rotation | Periodically, and after staff changes or suspected compromise |
| Revocation | Promptly when compromised |
| Archiving | Old keys kept as long as data encrypted with them must stay readable |
| Destruction | Securely deleted when no longer needed |
Segregation of duties applies: people who manage keys shouldn’t also have free access to the encrypted data. Master keys use split knowledge (nobody knows the whole key) and dual control (two people needed).
Example. A database is encrypted with AES-256, which sounds strong. But the key is in a configuration file on the same server, readable by the application account. An attacker who gets into the server gets both. The auditor recommends a key management service with separate access control.
Algorithms
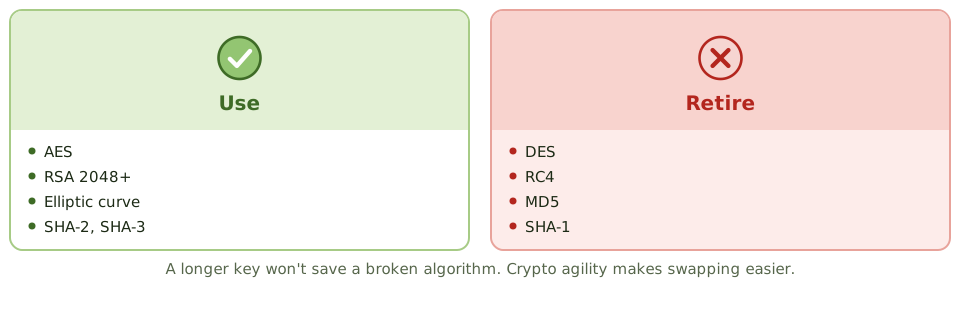
- Use current, approved algorithms: AES, RSA (2048 bits or more), elliptic curve cryptography, SHA-2 and SHA-3.
- Retire deprecated ones: DES, RC4, MD5, SHA-1. A longer key won’t save a broken algorithm.
- Crypto agility, being able to change algorithms without redesigning systems, matters more and more, especially with quantum-resistant algorithms on the way.
How the exam asks about it
| If the question asks… | The answer is usually… |
|---|---|
| Most common weakness in cryptographic systems | Key management |
| Technique providing non-repudiation | Digital signature |
| Where encryption keys should be stored | Separately from the data, in an HSM or key vault |
| Encryption for bulk data | Symmetric |
| Is hashing reversible | No |
In short
- Cryptography can provide confidentiality, integrity, authentication and non-repudiation, depending on the technique used.
- Symmetric encryption uses one shared key; asymmetric uses a public and private key pair; hashing produces a one-way fingerprint.
- The strength of encryption depends on the algorithm, the key length and, above all, how keys are managed.
- Key management covers generation, distribution, storage, use, rotation, revocation, archiving and destruction.
- Keys should be stored separately from the data they protect, ideally in hardware security modules or key management services.
- Weak or deprecated algorithms (DES, RC4, MD5, SHA-1) should be replaced; crypto agility makes that easier.
Exam traps
- Encryption alone doesn't give integrity or non-repudiation; digital signatures do.
- The most common weakness isn't the algorithm, it's key management.
- Keys stored on the same server as the encrypted data provide little protection if the server is compromised.
- Longer keys mean more resistance to brute force, but a broken algorithm stays broken.
- Hashing isn't encryption: it can't be reversed.
Slides
Click the slide and use the arrow keys. F toggles full screen.
What it can do
Three tools
Key management is where it fails
Algorithms