Topics in this domain
- Security Governance and Roles
- Data Classification and Ownership
- Security Policies
- Privacy Principles and GDPR
- Identity Management
- Authentication Factors
- Biometrics
- Access Models: DAC, MAC, RBAC
- Logical and Privileged Access
- Cryptography Basics
- Symmetric Encryption
- Asymmetric Encryption
- Hashing and Integrity
- Digital Signatures
- PKI and Certificates
- Firewalls
- IDS/IPS
- VPN, SSL/TLS, IPsec
- Wireless Security
- Endpoint and Mobile (BYOD)
- Cloud and Virtualization Security
- Physical Access Controls
- Environmental Controls: Fire, Power, HVAC
- Social Engineering
- Malware
- Network Attacks: DoS, Spoofing, Sniffing
- Application Attacks: SQLi, XSS
- Vulnerability Management and Pen Testing
- Incident Response
- Digital Forensics and Chain of Custody
- Security Awareness Training
- Logging, SIEM, and Auditing Security
Social Engineering
Hacking the person
Why pick a lock when someone will open the door for you? A confident person in a hi-vis vest carrying a ladder can walk into most buildings, and people will hold the door.
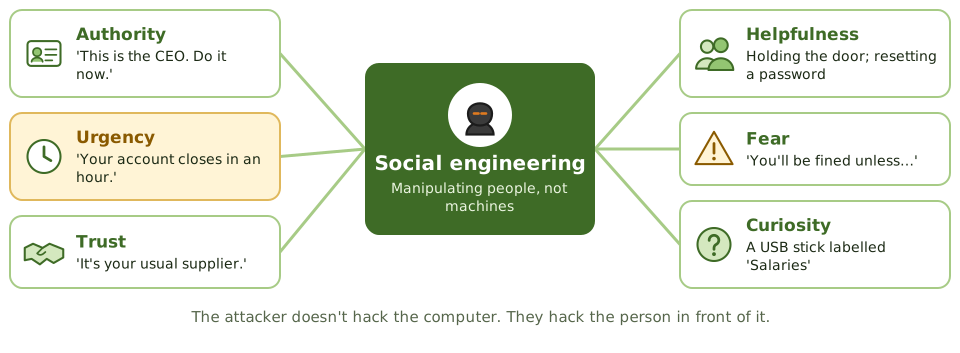
Social engineering exploits human behaviour rather than technical weaknesses. Attackers pull on authority, urgency, trust and helpfulness to get people to disclose information, grant access, run malware or send money.
The techniques
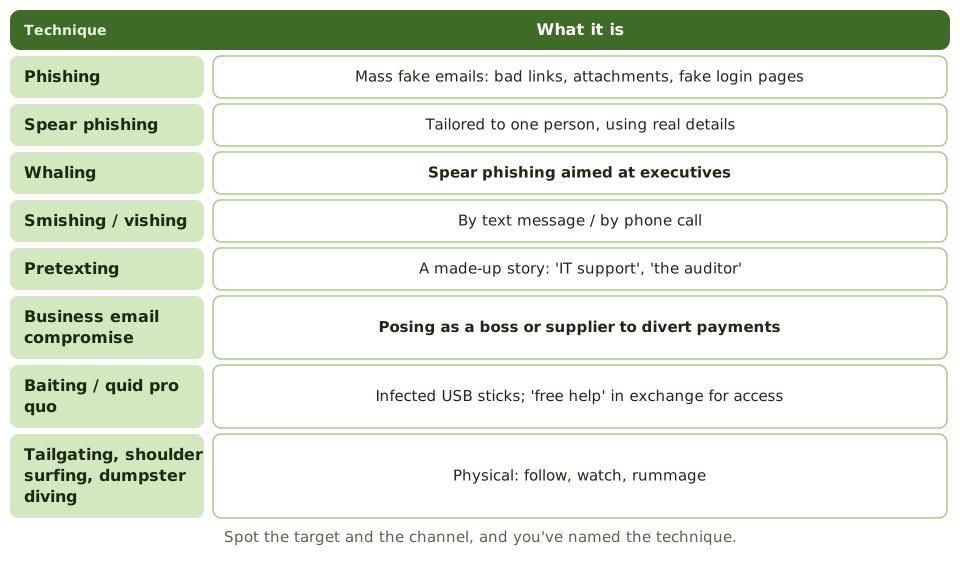
| Technique | What it is |
|---|---|
| Phishing | Mass fake emails with bad links, attachments or fake login pages |
| Spear phishing | Phishing tailored to one person, using real personal or company details |
| Whaling | Spear phishing aimed at senior executives |
| Smishing / vishing | Phishing by text message / by phone call |
| Pretexting | A made-up story, such as posing as IT support, a supplier or an auditor |
| Business email compromise (BEC) | Posing as an executive or supplier to request payments or bank detail changes |
| Baiting | Leaving infected USB sticks around, or offering “free” downloads |
| Quid pro quo | Offering something (like “IT help”) in exchange for information or access |
| Tailgating / piggybacking | Following an authorised person into a secure area |
| Shoulder surfing | Watching someone type a password or read sensitive data |
| Dumpster diving | Searching through thrown-away documents and media |
Business email compromise
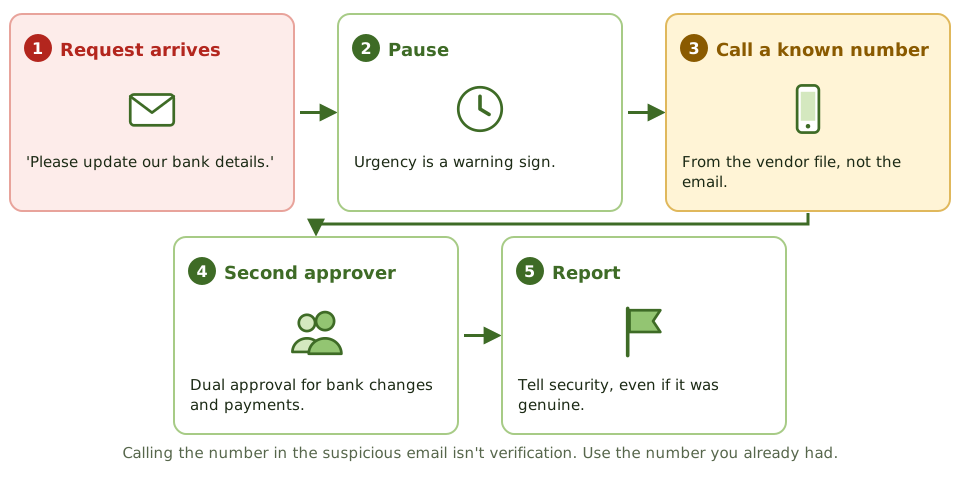
BEC is one of the costliest frauds. The key controls:
- independent verification of payment and bank detail changes, using a contact you already had (the vendor master file), never the number in the suspicious message
- dual approval for bank changes and payments
- a culture where pausing and checking is praised, not punished
Example. The accounts payable team gets an email from a known supplier asking to update bank details. It looks genuine because it comes from the supplier’s real, hacked mailbox. The clerk calls the supplier on the number in the vendor master file, not the one in the email, and learns it’s fraud.
What works
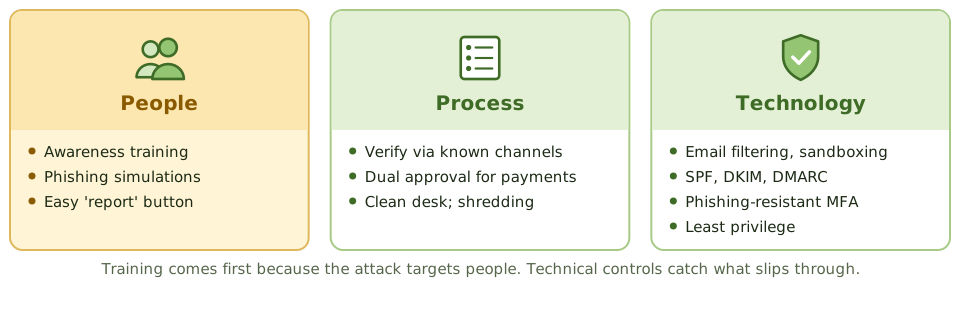
Security awareness training is the most effective control, because the attack targets people. Good programmes use realistic examples and phishing simulations, make reporting easy, and measure whether behaviour actually changes.
Supporting controls:
- verification procedures and dual approval, as above
- email security: filtering, attachment sandboxing, link protection, and SPF, DKIM and DMARC to stop others faking the organisation’s own domain
- phishing-resistant MFA, so a stolen password alone isn’t enough
- least privilege, limiting what a compromised account can do
- physical controls: mantraps, badges, escorts, clean desk, secure shredding
- easy reporting: a “report phishing” button and a quick response from security
How the exam asks about it
| If the question asks… | The answer is usually… |
|---|---|
| Most effective control against social engineering | Security awareness training |
| Best control against BEC payment fraud | Independent verification via known contacts and dual approval |
| Phishing aimed at executives | Whaling |
| Following an employee through a secure door | Tailgating / piggybacking |
| Control against dumpster diving | Secure disposal (shredding) and clean desk policy |
In short
- Social engineering manipulates people into revealing information, granting access or taking actions that benefit the attacker.
- Phishing uses fraudulent messages; spear phishing targets individuals; whaling targets executives; smishing and vishing use SMS and voice.
- Pretexting creates a believable scenario, such as posing as IT support or an auditor.
- Business email compromise (BEC) tricks staff into paying fraudulent invoices or changing bank details.
- Physical techniques include tailgating, shoulder surfing, dumpster diving and baiting with infected USB drives.
- The most effective control is security awareness training, supported by technical controls and verification procedures.
Exam traps
- Technical controls alone don't stop social engineering; awareness is the primary control.
- For BEC, the key control is independent verification of payment changes through a known contact channel, plus dual approval.
- Calling back a number provided in the suspicious message isn't independent verification.
- Phishing-resistant MFA limits the damage of stolen passwords.
- Clean desk and secure disposal policies counter dumpster diving.
Slides
Click the slide and use the arrow keys. F toggles full screen.
Hacking the person
Why pick a lock when someone will open the door for you? A confident person in a hi-vis vest carrying a ladder can walk into most buildings.
Social engineering exploits human nature, not technical flaws. Attackers lean on authority, urgency, trust and helpfulness to get people to hand over information, access or money.
The techniques
Business email compromise
What works